
In 2025, the cybersecurity landscape demands more than visibility—it demands intelligent action. As threats become increasingly advanced through automation, supply chain attacks, and AI-driven tactics, security teams require a SOC platform that cuts through the noise and enables them to operate with speed and confidence.
You can’t defend what you can’t see—and you can’t act on what you don’t trust.
Most solutions promise alerts. But Cyflare ONE delivers something better: a SOC platform built for actionable visibility and clarity in context, in real-time.
Clarity is no longer a nice-to-have
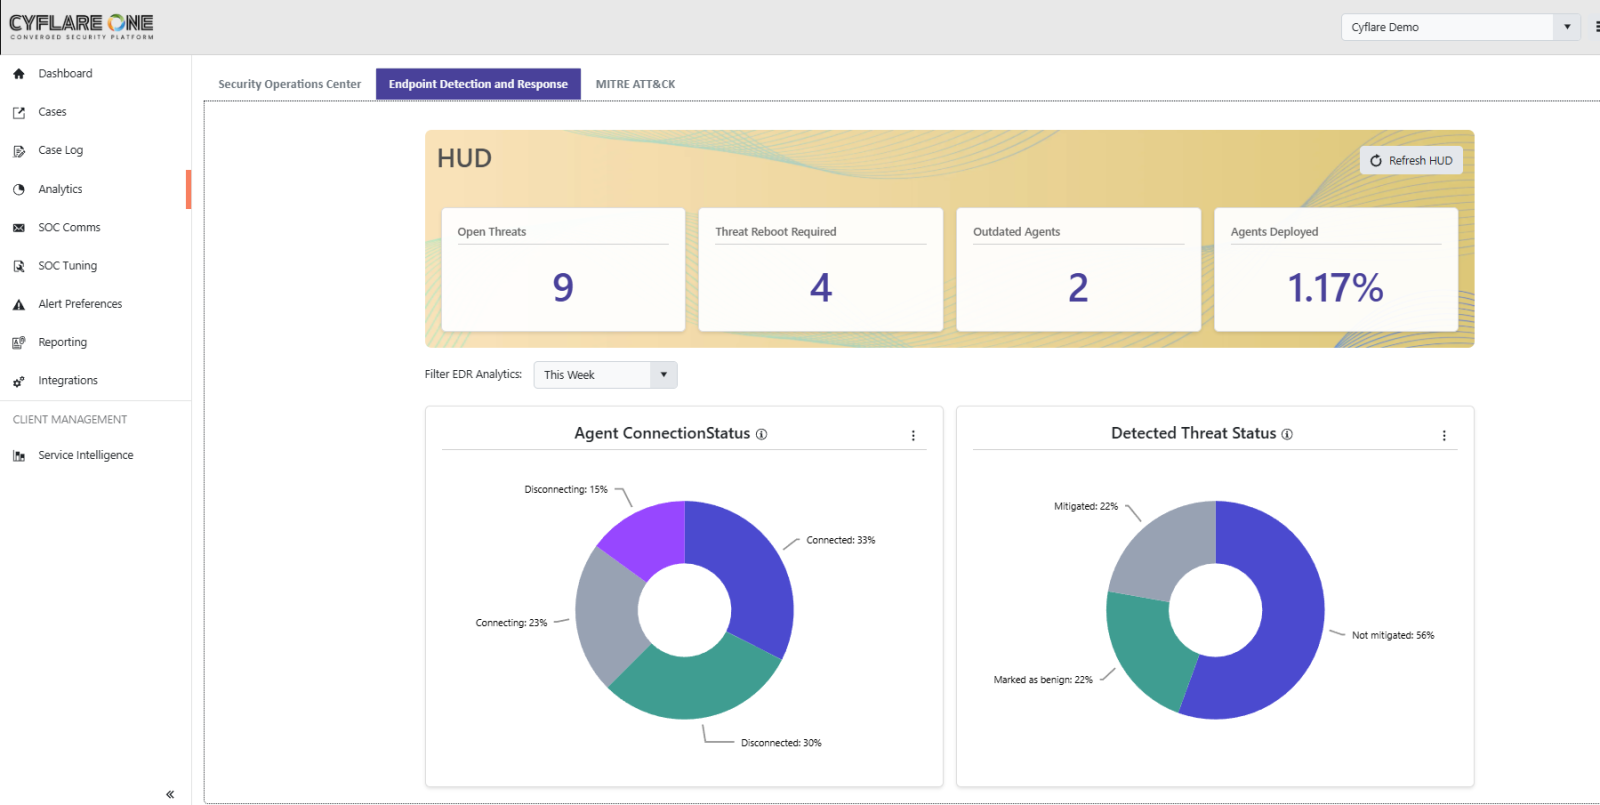
Security teams don’t struggle from a lack of alerts. They struggle with a lack of clarity about what’s real, what’s urgent, and what’s already been handled. Instead of asking analysts to parse thousands of raw events, ONE gives teams a live picture of SOC activity—what’s been auto-resolved, what’s escalated, and why.
Cyflare ONE helps reduce analyst fatigue by surfacing only the most relevant information and organizing it by impact. It’s accountability in action, and it’s visible in real time.
Threat visibility needs to evolve with the threats
The MITRE ATT&CK framework has become a modern standard for threat-informed defense. But coverage mapping shouldn’t live in spreadsheets or siloed audit reports. ONE makes it part of your daily workflow.
As a SOC platform, it visualizes observed vs. unobserved techniques across connectors, tools, and incident history. That means you don’t just see what happened—you can identify what didn’t. And that’s where the real risk lives.

Collaboration matters more than automation alone
We’re entering an era where the best SOCs don’t choose between humans and machines—they integrate both, intelligently. ONE’s in-app chat connects your team directly with Cyflare analysts, right inside the platform. Every action has traceability, and every SOC advisory, detection tuning, or threat escalation is logged, auditable, and shareable.
It’s not about replacing analysts. It’s about enhancing their focus with context, so they spend less time sorting signal from noise and more time stopping actual threats.
Metrics aren’t optional anymore
Leadership wants proof. Auditors want logs. Your team wants clarity. ONE gives all three. Dashboards built for security leaders let you track MTTD, MTTR, escalation rates, and ticket flow—all with filters for priority, resolution status, and ownership.
Cyflare ONE helps operationalize measurement with full transparency—from alerts to outcomes—so that strategic planning, compliance, and performance tracking are all aligned.

Built for scale, not just dashboards
Whether you’re delivering managed detection to 30 clients or running an internal SOC across business units, you can’t afford platform friction. ONE supports 350+ integrations, full multi-tenant isolation, and customizable workflows across detection, escalation, ticketing, and reporting.
And because it’s cloud-native, updates, tuning, and advisory delivery happen at the pace your threats evolve, not weeks later.
Final thought
Most cybersecurity platforms were built to react. Cyflare ONE was built to drive clarity—across every detection, decision, and report. In a world where threats don’t wait, your SOC platform shouldn’t either.
Want to see ONE in action?
👉 Schedule your personalized walkthrough


